Red Teaming Services
Your penetration tests may pass and your security tools may be running, yet it is hard to know whether your team would notice a patient attacker moving from one system to the next. Our red teaming services answer that question through a controlled red team assessment, agreed in advance and run within a defined scope. Using red team security testing against realistic scenarios, we help security and IT leaders see where prevention, detection and response work and where they need attention. You receive evidence-backed findings and a clear debrief your teams can act on, so effort and budget go to the fixes that reduce risk most. Everything is authorized in writing and kept within limits you set, so your day-to-day operations stay protected.
What Do Red Teaming Services Include?
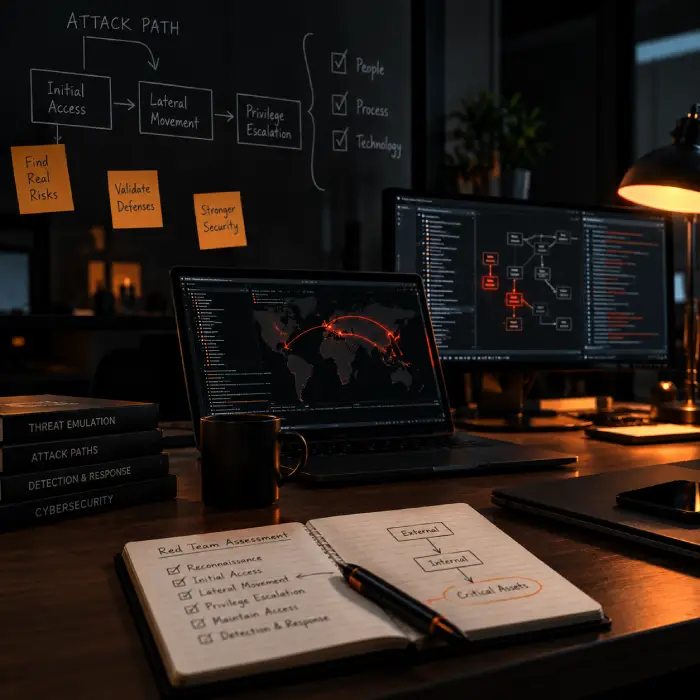
Red teaming is an authorized exercise in which a security team imitates the methods of a realistic adversary to test an organization's defenses. NIST's glossary describes a red team as a group authorized and organized to emulate an adversary's attack capabilities against an organization's security posture. The goal is to learn what works for defenders and what does not, in your actual environment. A red team security assessment usually combines the activities below. The exact mix is set during scoping, based on your objectives and risk appetite.
A red team security assessment usually combines the activities below:
- Scoping, objectives, and written rules of engagement, agreed before any testing starts.
- Threat-informed planning, so scenarios reflect adversary behavior relevant to your business.
- Adversary simulation services that follow an attack path across external, internal, identity, and cloud layers where in scope.
- Observation of how your monitoring, alerting and incident response react.
- Social engineering or phishing exercises, only where explicitly authorized.
- Evidence-backed findings, prioritized recommendations and a debrief with your teams.
- Retesting of fixes, where included in the agreed scope.
Why Businesses Invest in Red Teaming Services
Security tools and policies show what you have deployed. They do not always show how it behaves under pressure. Red teaming gives leaders evidence of how controls perform together, so budget and effort go where they matter. Results depend on scope and maturity, and no exercise can guarantee that an incident will be prevented.
Evidence of How Controls Perform
Security control validation shows whether tools and policies work in practice, not just on paper.
Attack Paths Across Systems
Issues that look minor alone can connect. Seeing the chain helps you fix the link that matters most.
Detection and Response Under Test
See whether alerts fire, who sees them, and how quickly your team acts.
Remediation That Follows Risk
Findings backed by demonstrated impact make it easier to rank fixes and justify the work.
Stronger Security and IT Coordination
Threat-led security testing ends with a shared debrief, so offensive findings turn into defensive improvements your teams agree on.
Red Teaming Solutions Built for Your Business
Our red teaming consulting services can combine the engagement scopes below, depending on your objectives, environment, and rules of engagement. We agree on the final selection with you during scoping.
External Attack Simulation
Tests what an outside attacker could reach through your internet-facing systems and staff, and whether your team notices the attempt.
Internal Network and Identity Assessment
Starting from an assumed foothold, we assess how far a user account could move, including privilege escalation testing, Active Directory and access-control weaknesses.
Adversary Emulation
Scenarios modeled on the behavior of threat actors relevant to your sector, so you test against realistic methods rather than generic checklists.
Cloud Security Attack Simulation
Examines cloud accounts, roles, and configurations for paths between workloads and data, where cloud is in scope.
Detection and Response Validation
Checks whether your SOC, SIEM rules, and endpoint tools detect the simulated activity, and how your incident response plays out.
Social Engineering Assessment
Authorized phishing and pretexting exercises show how staff and processes handle deceptive requests, with results shared as learning, not blame.
Security Control Validation
Targeted attack simulation services that confirm whether specific controls, such as email filtering or endpoint protection, behave as intended.
Purple Team Collaboration
Offensive and defensive teams work side by side to tune detections while the exercise runs, shortening the loop between finding and fixing.
Continuous or Repeat Exercises
A recurring schedule of smaller exercises can track improvement over time, suited to organizations with a mature security program.
Want to Know How Your Defenses Would Respond?
Tell us what you need to learn, such as detection, identity or cloud exposure. We will help you match our red teaming solutions to a red team assessment scope that fits.
Our Red Teaming Process
Your security and business priorities guide every stage of our red teaming process. We begin only after receiving your written authorization, with clearly defined scope, testing boundaries, and objectives. We then agree on a practical testing plan and timeline based on your environment, security requirements, and the questions you need answered.
- 1
Objectives and Scope Definition
We agree on what you want to learn, which systems, people and locations are in scope, and what is off limits.
- 2
Rules of Engagement and Authorization
Written authorization, contacts, testing windows, escalation paths, and safeguards are signed off before testing begins.
- 3
Threat-Informed Planning
We design scenarios using relevant adversary emulation techniques, often mapped to the MITRE ATT&CK knowledge base.
- 4
Controlled Testing
Scenarios run within the agreed limits, with stop conditions and a named contact to pause if business operations are at risk.
- 5
Analysis and Prioritization
We review evidence, trace attack paths, and rank findings by demonstrated impact on your objectives.
- 6
Reporting, Debrief and Validation
You receive a written report and a walkthrough with your teams. Retesting of fixes is available where included in scope.
Red Teaming Services Use Cases
Explore common red teaming services use cases where a red team assessment helps uncover security gaps that routine testing may miss. From testing incident response to simulating real-world cyberattacks, red teaming helps organizations evaluate their defenses, identify weaknesses, and strengthen their overall security posture.
Security Monitoring and Alert Validation
Find out whether your monitoring tools and SOC pick up simulated attacker activity, and how quickly an alert turns into action.
Identity-Based Attack Path Assessment
See how far a single compromised account could travel, and which permissions or misconfigurations let it reach sensitive systems.
Incident Response Readiness Testing
Put your response plan under realistic pressure to confirm that roles, escalation, and handoffs work, and strengthen your incident response readiness before a real event.
Hybrid and Cloud Exposure Assessment
Trace attack paths across on-premises systems, cloud accounts and third-party connections, where gaps often sit between teams.
Security Control Effectiveness Testing
Confirm that your endpoint, email, network, and identity controls block or flag attacker behavior, and see where they leave gaps.
Threat-Informed Defense Assessment
Measure your defenses against the adversary techniques most relevant to your industry, planned with a recognized framework such as MITRE ATT&CK.
Offensive and Defensive Team Collaboration
Bring your security and IT teams together in joint review sessions, so findings become better detections and updated playbooks.
Remediation Validation and Retesting
Re-run earlier scenarios after fixes are made to confirm the weakness is closed and the improvement holds.
Red Teaming vs Penetration Testing, Vulnerability Assessment and Purple Teaming
Red teaming is one of several offensive security services. They answer different questions, and real engagements often blend them. Many organizations use several over time. The table shows typical differences, not fixed rules.
| Dimension | Red Teaming | Penetration Testing | Vulnerability Assessment | Purple Teaming |
|---|---|---|---|---|
Primary objective | Test whether a realistic attacker can reach a goal and whether defenders respond | Find and prove exploitable weaknesses in defined systems | Identify and rank known weaknesses broadly | Improve detection by running attacks with defenders |
Typical scope | People, process and technology, set by objective | Specific applications, networks or environments | Wide set of assets, often scanned | Chosen techniques and detections |
Testing approach | Objective-driven scenarios, often with limited notice to defenders | Targeted, usually known to the security team | Mostly automated scanning with validation | Open, collaborative and iterative |
Attack-path focus | High | Medium | Low | Medium |
Detection and response focus | High | Usually limited | Not tested | Very high |
Typical output | Attack narrative, findings, detection gaps, recommendations | Technical findings with severity and fixes | Prioritized list of weaknesses | Tuned detections and shared lessons |
Best fit | Mature programs testing end-to-end resilience | Validating a system before or after release | Routine hygiene and coverage | Teams building detection capability |
Technologies We Use to Build Red Teaming Solutions
These are the frameworks and technology categories a red team assessment typically involves. We confirm the specific tooling for your engagement during scoping, based on your environment and rules of engagement.
Industries We Help With Red Teaming
Why Choose Wappnet AI as Your Red Teaming Company?
When choosing a red teaming company, buyers want clear scope, safe testing and findings their teams can act on. Our approach is built around those three things, and draws on Wappnet.ai's broader engineering and AI work. We keep you informed at every stage, so there are no surprises when the report arrives.
Scope Agreed First
Objectives, boundaries and authorization are written down before testing starts, and you can adjust scope as the work progresses.
Findings Your Teams Can Use
Reports are written for executives and engineers, with evidence, priorities and a debrief to walk through them.
Built for Modern Environments
Our engineering background covers cloud, data and AI-enabled systems, which helps when attack paths cross several platforms.
Connected to Wider Delivery
Findings can feed into engineering fixes and governance work. See Responsible AI and EU AI Act.
Real-World Red Teaming Solutions We've Delivered
Realistic adversary simulations delivering validated detection capabilities, hardened identity architectures, and actionable remediation across enterprise infrastructure.
Multi-Stage Cloud & On-Premises Lateral Movement Simulation
Testing an assumed-breach scenario traversing Active Directory hybrid identity into AWS production workloads.
Joint Purple Teaming & SOC Detection Engineering
Collaborative adversary emulation to validate SIEM alerting rules, tune EDR policies, and close logging visibility gaps.
Privilege Escalation & Ransomware Attack Path Hardening
Evaluating identity attack paths, service account permissions, and segmentation to prevent enterprise-wide compromise.
Ready to Define the Right Scope?
Whether you are shortlisting a red teaming company or already know what you need, share your security objectives, environment and constraints. We will talk through what an appropriate assessment could look like.
Latest AI Insights & Industry Trends
 RAG
RAG vs Fine-Tuning vs Prompt Engineering: Which Approach Fits Your Use Case?
Compare RAG, fine-tuning, and prompt engineering to explore costs, use cases, and the best approach for enterprise AI.
 AI Copilot
What is an AI Copilot? Use Cases & Build Guide
What is an AI Copilot? Learn how it works, how it differs from AI agents, key use cases, and how to build one for your business.
 RAG
What Is RAG? A Complete Guide to Retrieval-Augmented Generation
Learn what RAG is, how Retrieval-Augmented Generation works, reduces AI hallucinations, and powers smarter enterprise AI.
Frequently Asked Questions
Red teaming services are authorized security exercises in which specialists imitate realistic attackers to test your defenses. They cover people, processes and technology, and show whether your team can prevent, detect and respond to an attack aimed at a defined objective.
A red team assessment starts with agreed objectives and written rules of engagement. The team then plans scenarios based on relevant adversary behavior, runs them under controlled conditions, records what happened and reports findings. A debrief with your security and IT teams turns results into fixes.
It typically includes scoping, rules of engagement, threat-informed planning, simulated attack activity, observation of detection and response, a written report with prioritized recommendations and a debrief. Social engineering, cloud testing or retesting are added only when agreed in scope.
Penetration testing looks for exploitable weaknesses in defined systems, while red teaming tests whether an attacker can reach an objective and whether your defenders notice. Red teaming is broader and goal-driven, and the two often complement each other.
A vulnerability assessment lists and ranks known weaknesses across many assets, usually with automated scanning. Red teaming does not aim for a complete list. It tests how weaknesses, access and detection gaps combine in a realistic attack.
Red teaming tests defenses with limited notice to defenders, while purple teaming has attackers and defenders work together openly to improve detections. Many organizations run a red team exercise and follow it with a purple team session.
It depends on scope, environment size and how stealthy the simulation must be. Providers publish ranges from a couple of weeks for tightly scoped exercises to several months for full, no-prior-knowledge operations. We give a plan after scoping rather than a fixed number in advance.
Cost depends on scope, duration, team size, the number of scenarios, whether physical or social engineering testing is included and the reporting and retesting you need. We provide an estimate after scoping so you can compare options.
There is no universal schedule. Many organizations repeat exercises when their environment changes significantly or after major fixes, and mature programs may run smaller exercises more often. Your risk profile and any regulatory expectations should guide the interval.
Yes, this is one of its main purposes. Exercises show whether alerts fire, who sees them, how quickly the team acts and whether playbooks work in practice. Results can then be used to tune detections and refine response plans.
Testing follows written rules of engagement that define scope, timing, off-limit systems, escalation contacts and stop conditions. A named contact on your side can pause activity at any time. Even so, no offensive testing is entirely risk-free, so the plan covers safeguards in advance.
When choosing a red teaming company, look for clear scoping and authorization practices, evidence of relevant experience, transparent reporting and a debrief that your teams can act on. Ask how the provider limits risk to operations and what happens after the report, including retesting.