Data Governance, Security & Compliance Solutions
Different teams own different pieces of the same data; nobody can say with confidence where sensitive information actually lives, and every access review or audit request turns into a multi-week scramble across disconnected systems. Data Governance, Security & Compliance solutions from Wappnet.ai help you bring ownership, access control, and audit readiness together, so data across your business is more trustworthy, more appropriately secured, and easier to account for, without promising that a single tool will solve every governance problem on its own.
Why Businesses Invest in Data Governance, Security & Compliance
Interest in Data Governance Solutions rarely starts with a regulation alone. It usually starts with one specific, recurring operational problem. Not every business hits every challenge below, and not every organization needs the same level of Enterprise Data Governance to address the ones it does face.
Unclear Data Ownership and Stewardship
When nobody is formally accountable for a dataset, decisions about its quality, access, and retention default to whoever touches it last, and issues go unresolved because no one feels responsible for fixing them.
Inconsistent Policies Across Departments and Systems
Each team applies its own rules for retention, sharing, and classification, so a single business policy can mean three different things depending on which system you're looking at.
Limited Visibility Into Sensitive Data
Sensitive fields accumulate in spreadsheets, logs, and secondary systems that were never scanned, so a business can't reliably answer where its sensitive data actually lives until something forces the question.
Excessive or Outdated Access Permissions
Access gets granted for a project and never revoked; roles change, but permissions don’t follow, and over time far more people can reach sensitive data than actually need to.
Fragmented Metadata and Data Lineage
Without a record of where data came from and how it was transformed, teams can't confirm whether a number in a report traces back to a trustworthy source or a long-forgotten workaround.
Inconsistent Classification and Retention Practices
Data gets kept indefinitely because deleting it feels risky, or deleted inconsistently because no retention schedule was ever agreed upon, leaving both unnecessary exposure and gaps in records.
Manual Evidence Collection and Audit Preparation
When an auditor or regulator asks a specific question, answering it means pulling together spreadsheets, emails, and tribal knowledge rather than consulting a documented, current record.
Unclear Accountability for Analytics and AI Data
An AI or analytics initiative draws on data nobody has formally reviewed for ownership, quality, or appropriate use, which makes it harder to explain or trust the resulting output.
What Does a Data Governance, Security & Compliance Solution Include?
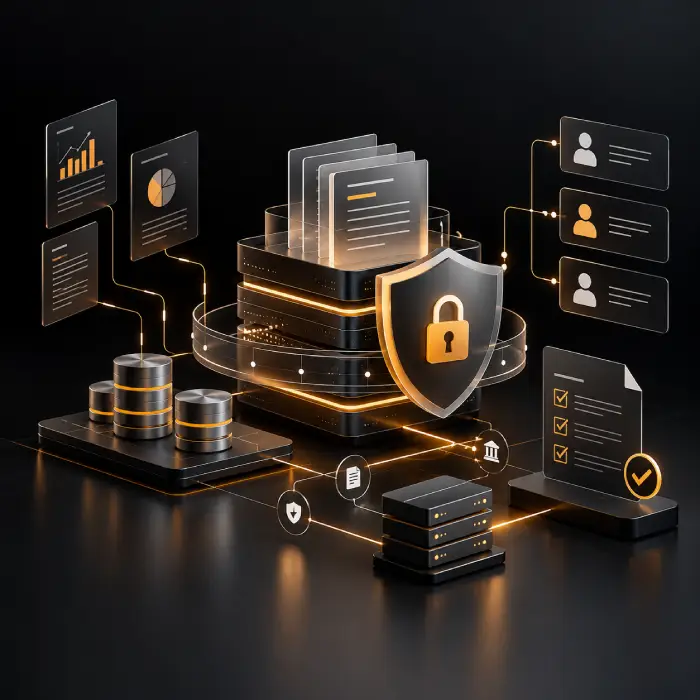
These are related but distinct disciplines. Data governance covers policy, ownership, stewardship, and classification. Data security covers identity, access controls, and protection against unauthorized use. Data privacy covers how personal or sensitive data is collected, used, and retained. Data compliance covers the processes that support legal and regulatory obligations. No single tool makes an organization compliant on its own; these capabilities work together across the data lifecycle.
- We run Sensitive Data Discovery across databases, cloud storage, and business applications to identify what data exists and where it lives.
- We apply Data Classification and Cataloging with sensitivity labeling so every critical dataset has a clear, accountable owner.
- We build Data Lineage and Metadata Management so teams can trace where data originated and how it moved.
- We design Data Access Control on identity, role-based permissions, and least-privilege principles.
- We define Data Lifecycle Management for retention, archival, and deletion, backed by Data Privacy and Security safeguards.
- We put Data Audit and Monitoring in place so evidence is available before an audit request ever arrives.
- We extend Data Governance for AI and analytics so model and dashboard data carries the same ownership and traceability as everything else.
Data Governance, Security & Compliance Solutions Built for Your Business
Every organization has different data risks, systems, and governance requirements. Wappnet.ai develops Data Governance and Security Solutions around your existing environment, helping you establish clear ownership, protect sensitive information, and maintain visibility into how data is accessed and used. The right combination of capabilities depends on your business priorities, technical landscape, and regulatory obligations.
Establishing Enterprise-Wide Data Governance
A practical Data Governance Framework defines who owns critical datasets, who can make decisions about them, and how policies are maintained across departments. We help establish governance roles, stewardship responsibilities, and decision-making processes that fit your organizational structure.
Improving Sensitive Data Discovery and Classification
When sensitive information is scattered across databases, cloud storage, and business applications, visibility becomes a challenge. Our approach combines data discovery with classification and sensitivity labeling to help security and data teams identify important information and prioritize protection efforts.
Standardizing Data Access and Ownership
Data access should reflect current responsibilities, not permissions accumulated over time. We help design Data Access Governance around role-based permissions, least-privilege principles, and periodic access reviews, with clear responsibilities for approving and maintaining access.
Strengthening Cloud Data Governance
Organizations using multiple cloud platforms need consistent governance without losing sight of platform-specific capabilities. Our Cloud Data Governance approach aligns classification, access, metadata, and retention policies across cloud and on-premises environments while accounting for differences between systems.
Improving Data Lineage and Auditability
When teams cannot trace where information originated or how it was transformed, reporting and audit investigations become harder. We help establish metadata management and data lineage for critical assets, making data flows easier to understand and supporting more efficient evidence gathering.
Establishing Privacy and Retention Workflows
Keeping sensitive information longer than necessary can increase exposure, while premature deletion can create operational and recordkeeping problems. Our Data Protection and Compliance approach helps define retention schedules, archival rules, and deletion workflows in line with applicable business and legal requirements.
Governing Data for Analytics and AI
Analytics and AI initiatives need clear information about dataset ownership, quality, origin, and permitted use. We incorporate AI Data Governance into relevant data workflows so teams can assess data suitability, trace its origins, and document how it is intended to be used.
Addressing Governance Gaps Across Multiple Systems
Legacy databases, modern cloud platforms, and departmental applications often maintain separate policies and records. We help connect governance processes across these environments, prioritizing critical systems and closing gaps without assuming that the organization must replace its existing platforms.
Review Your Data Governance Priorities
Tell us about your current data ownership gaps, sensitive-data visibility, access management challenges, or audit readiness, and we'll help map what a practical Data Compliance Solutions approach looks like for your business.
Works With the Tools You Already Use
Our data governance and security solutions are designed to work alongside your existing platforms, databases, and identity systems. The right integration approach depends on your current environment and technical requirements.
Our Data Governance, Security & Compliance Process
A practical path from understanding your data environment to validated, monitored controls, built around your systems and obligations, not a one-size-fits-all rollout.
- 1
Assess the Data Environment and Business Risks
We review your current systems, existing controls, and risk priorities. You share context on your data landscape and obligations; we evaluate where the gaps and highest-risk areas actually are.
- 2
Discover and Classify Relevant Data
We inventory data across your environment and apply classification and sensitivity labels. You provide access to relevant systems; we deliver a documented data inventory and classification baseline.
- 3
Define Ownership, Policies, and Governance Priorities
We work with your stakeholders to assign stewardship and set policy priorities as part of a Data Governance Strategy. You confirm business ownership; we document decision rights and accountability.
- 4
Design Access Controls and Protection Measures
We design role-based, least-privilege access and relevant protection measures matched to data sensitivity. You validate role definitions; we evaluate technical feasibility within your platforms.
- 5
Implement Governance Workflows and Technical Controls
We implement agreed controls, catalogs, and workflows as part of Data Governance Policy Implementation. You participate in validation; we confirm controls function as designed before go-live.
- 6
Validate Controls, Monitor Activity, and Improve Continuously
We validate monitoring, review exceptions, and support Data Risk Management on an ongoing basis. You review reporting on a set cadence; we adjust controls as the environment and obligations change.
Data Governance, Security & Compliance: Use Cases
Data governance becomes valuable when teams can find the information they need, understand who is responsible for it, and use it with appropriate controls. These use cases illustrate how better governance can address everyday operational challenges across an organization.
Sensitive Data Discovery and Classification
Security teams need to know where customer records, financial details, and other sensitive information are stored before they can protect them effectively. A documented inventory helps identify overlooked data stores and gives teams a clearer starting point for prioritizing security controls.
Enterprise Data Ownership and Stewardship
When a critical dataset has no clear owner, quality problems and access requests can remain unresolved. Assigning responsibility gives business and data teams a clear point of contact for decisions about accuracy, access, and retention.
Data Access Governance
Employees change roles, projects end, and external collaborators move on. Regular access reviews help organizations identify outdated permissions and ensure people retain access only when they have a legitimate business need.
Data Lineage and Audit Traceability
When a report contains an unexpected figure, analysts need to understand where it came from and which transformations affected it. Documented lineage helps data and compliance teams investigate discrepancies and prepare supporting evidence without reconstructing every step manually.
Cloud Data Governance Across Platforms
Teams working across multiple cloud environments can struggle with inconsistent access rules and data classifications. Shared governance policies help establish a more consistent approach while allowing technical teams to account for each platform’s capabilities.
Privacy and Retention Workflows
Legal, privacy, and operational teams need clarity about how long personal and sensitive information should be retained. Documented retention and deletion workflows help make these decisions repeatable and reduce reliance on informal practices.
Data Quality Accountability
When dashboard figures conflict or records contain errors, teams need to know who is responsible for investigating and correcting the problem. Defined ownership and quality rules help route issues to the right people instead of allowing workarounds to become permanent.
Regulatory Evidence Preparation
Audit requests often require teams to locate policies, access records, and information about data flows. Maintaining organized governance documentation makes relevant evidence easier to retrieve and reduces the pressure of assembling records at the last minute.
Governance for Analytics and AI Data
Data scientists and analytics teams need to understand whether a dataset is suitable for a particular use and what limitations apply. Clear ownership, documented origins, and data quality information support more informed decisions before data enters analytical workflows or AI applications.
Data Sharing Across Departments and Hybrid Environments
Different departments may maintain overlapping datasets because they cannot easily discover or access information already available elsewhere. Better cataloging, ownership, and access workflows help teams find reusable data while preserving appropriate controls across on-premises and cloud systems.
Data Governance, Security & Compliance: Comparing Approaches
These three approaches to Data Governance and Security Solutions aren’t interchangeable, and the right fit depends on your data sensitivity, system complexity, and obligations, not a universal ranking.
Industries We Help With Data Governance, Security & Compliance Solutions
Data sensitivity and regulatory context differ by industry, so governance work is scoped per business, not a single template, and no implementation by itself satisfies any specific industry regulation.
Financial Services & Banking
Transaction, account, and customer data governed with ownership, access control, and lineage suited to financial oversight expectations.
Healthcare & Life Sciences
Clinical and patient data classified and access-controlled with privacy considered throughout the data lifecycle, not applied afterward.
Retail & Ecommerce
Customer and transaction data governed for consistent access and retention across channels, platforms, and marketing systems.
Manufacturing & Industrial Operations
Production, quality, and supplier data cataloged and access-controlled so operational and compliance teams can trust what they're reviewing.
Technology & SaaS
Customer, usage, and product data governed with clear ownership as the business scales and data volume and user base grow.
Logistics & Supply Chain
Shipment, partner, and inventory data governed consistently across internal systems and external partner integrations.
Professional Services
Client, engagement, and billing data governed with access control and retention appropriate to client confidentiality expectations.
Insurance
Policy, claims, and underwriting data classified and governed with access, retention, and audit trails suited to regulatory scrutiny.
Why Choose Wappnet AI for Data Governance, Security & Compliance Solutions?
Wappnet.ai approaches governance as part of a broader data engineering practice, understanding your existing environment and workflows before recommending changes. Whether you're looking for a focused Data Governance Consulting engagement or an ongoing Data Governance Services partnership, or evaluating us as a Data Governance Company for a specific initiative, we scope the engagement to match your priorities rather than applying a fixed package.
- Understand your existing data environment and controls before recommending any change.
- Align governance controls with real business workflows, not just policy documents.
- Connect data architecture, quality, access, and lifecycle considerations as one coherent program.
- Design around your existing platforms where practical, rather than assuming a replacement.
- Support implementation and iterative improvement, not a one-time policy rollout.
- Extend governance to analytics and AI data in coordination with our responsible AI development practice where relevant.
- Explain clearly what a control can and cannot guarantee, rather than overstating compliance outcomes.
Real-World Data Governance, Security & Compliance Solutions We've Delivered
Explore how leading organizations transform fragmented access and compliance burdens into automated, audit-ready data governance programs.
Enterprise Sensitive Data Discovery & Classification
Automated continuous sensitive data discovery across 20+ multi-cloud and on-prem databases for a global fintech, reducing audit preparation time from weeks to hours.
Healthcare HIPAA-Compliant Data Access Governance
Designed least-privilege role-based access controls and automated periodic entitlement reviews for a healthcare network, eliminating over 1,500 dormant high-risk permissions.
Cloud Data Lineage & Metadata Architecture for Retail
Implemented automated end-to-end data lineage across Snowflake and Databricks, providing verifiable traceability for regulatory financial reports and customer analytics.
Strengthen Data Governance, Security & Compliance Across Your Business
Our team can help assess your current data ownership, sensitive-data visibility, access controls, and audit readiness, before any commitment to build a program.
Latest AI Insights & Industry Trends
 RAG
RAG vs Fine-Tuning vs Prompt Engineering: Which Approach Fits Your Use Case?
Compare RAG, fine-tuning, and prompt engineering to explore costs, use cases, and the best approach for enterprise AI.
 AI Copilot
What is an AI Copilot? Use Cases & Build Guide
What is an AI Copilot? Learn how it works, how it differs from AI agents, key use cases, and how to build one for your business.
 RAG
What Is RAG? A Complete Guide to Retrieval-Augmented Generation
Learn what RAG is, how Retrieval-Augmented Generation works, reduces AI hallucinations, and powers smarter enterprise AI.
Frequently Asked Questions
Governance sets ownership and policy for data, security controls who can access or change it, and compliance covers the processes that support legal and regulatory obligations. Together they help a business know what data it has, who’s accountable, and whether it can prove that on request.
Governance defines ownership, policy, and accountability; security enforces who can actually access, modify, or extract the data. Effective programs design both together.
A Data Governance Framework gives a consistent way to assign ownership, classify data, and set retention standards instead of handling every dataset differently. Without one, accountability gets unclear as the organization grows.
Through a discovery process that inventories data across databases, cloud storage, and applications, then applies classification and sensitivity labels. This needs periodic rescanning, since new sensitive data keeps appearing.
By pairing data classification with role-based, least-privilege access controls that are reviewed on a schedule and logged when they change.
Lineage traces where data came from and how it moved, so teams can trust it and compliance can answer where it originated. It turns a compliance request into a documented answer instead of a lengthy investigation.
By applying consistent classification, access, and retention policies across every cloud and on-premises system, usually through a central policy layer or catalog with monitoring.
Data Governance for AI documents which datasets are approved for which uses and who owns them. It doesn’t make an AI output accurate or compliant by itself, but gives teams a traceable foundation to evaluate.
Common indicators include owner coverage for critical datasets, the percentage of sensitive data classified, access review completion rates, and time to locate audit evidence, tracked over time rather than against fixed targets.
No. Controls support compliance activities but don’t guarantee it on their own. Obligations depend on your jurisdiction, industry, and data types, and require qualified legal advice.
By assessing the current environment and risk priorities, then discovering and classifying data, defining ownership, and designing access controls before enforcement. Starting with the highest-risk data tends to move fastest.
In most cases, yes. They’re generally designed to work alongside your existing databases, cloud platforms, and identity systems, though the integration effort varies by platform.